
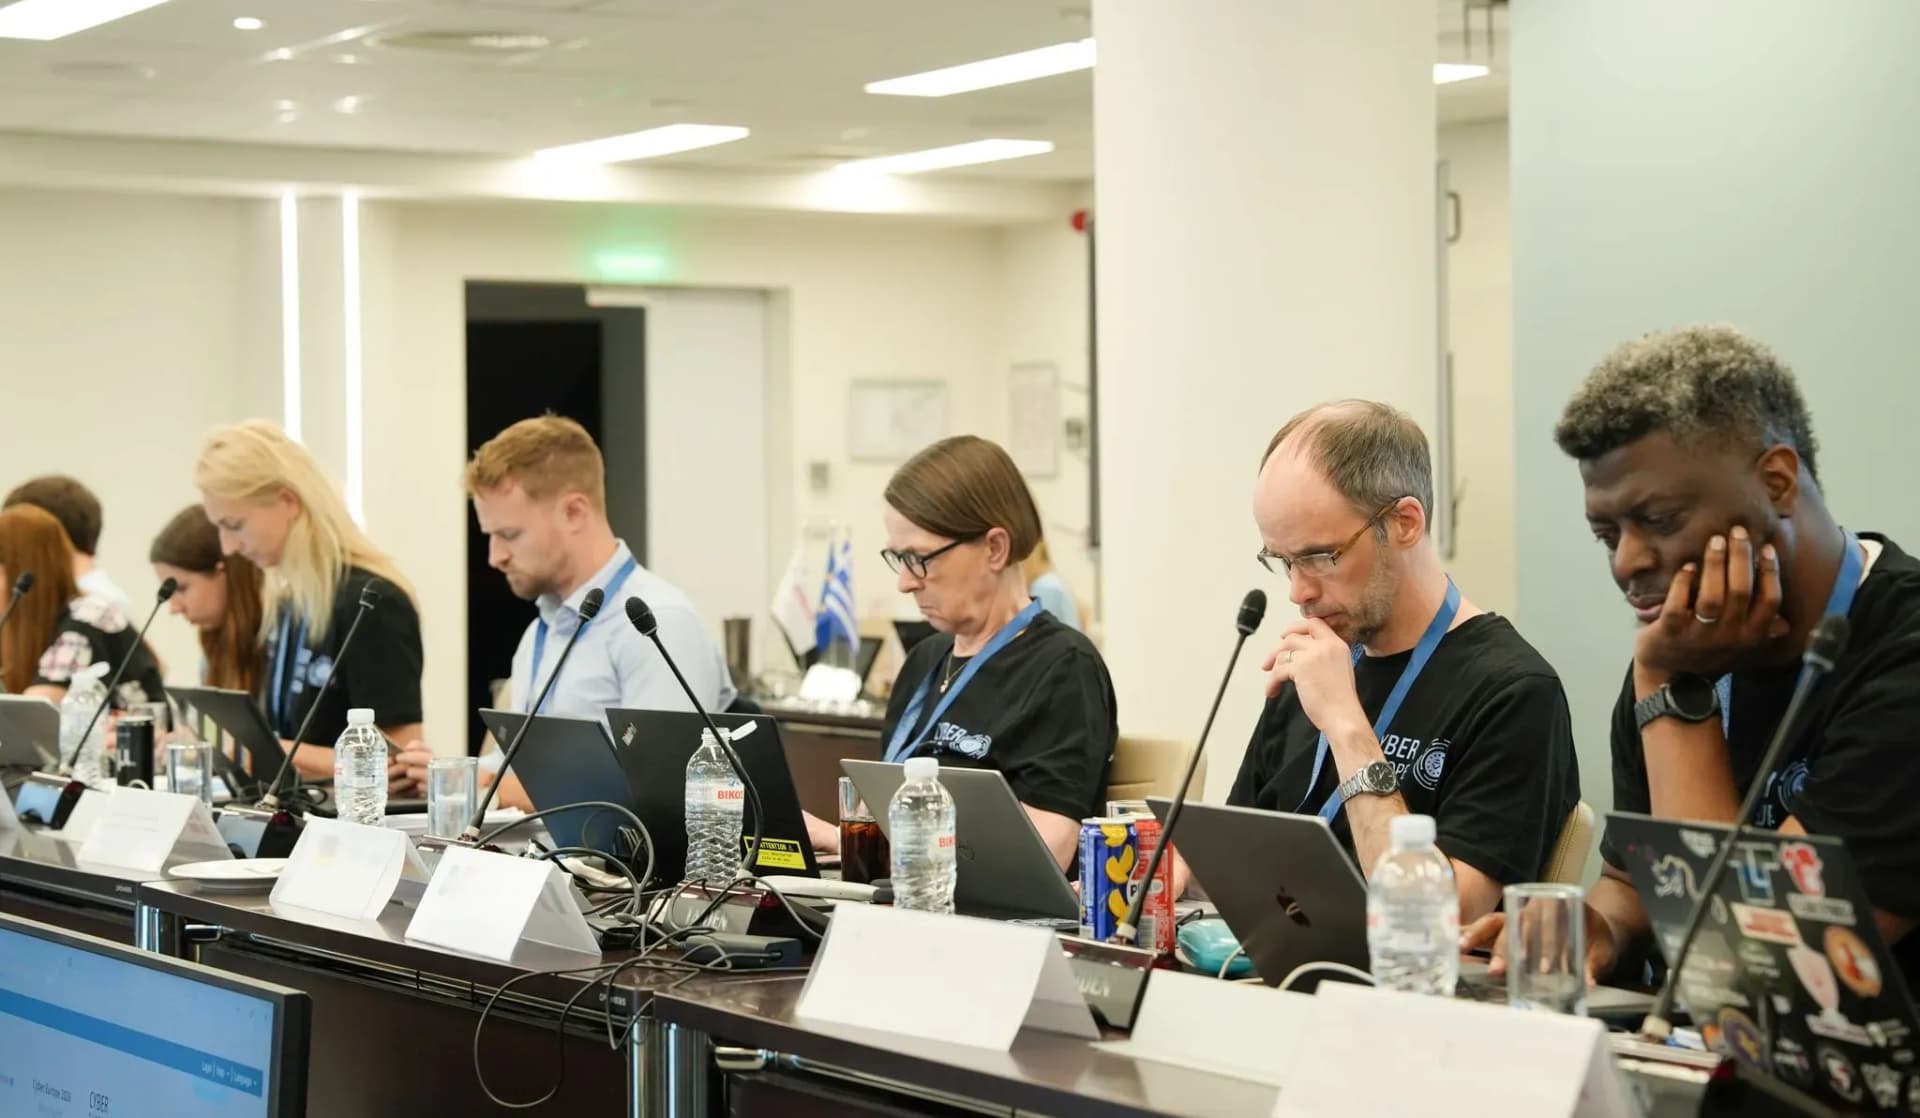
The European Union Agency for Cybersecurity (ENISA) coordinated the eighth edition of the Cyber Europe exercise on June 10 and 11, aiming to improve preparedness for digital incidents and ensure the continuity of essential services in the continent's railway and maritime networks.
The two-day drill simulated large-scale cyber incidents that led to a systemic crisis for the interconnected transport systems of the European Union. Participants had to analyze advanced technical incidents under the pressure of complex scenarios inspired by real threats. The central activity was based on the exchange of information among the actors involved to maintain situational coverage at technical, operational, and political levels. ENISA collaborated with over 100 experts from national cybersecurity agencies, public and private sectors of the EU, and the European Free Trade Association (EFTA), totaling more than 5,000 participants.
The Executive Vice President for Technological Sovereignty, Security, and Democracy, Henna Virkkunen, has pointed out that transport is a critical sector vulnerable to cyber threats. According to the community representative, incidents at ports or railways cause effects that extend beyond the sector itself, affecting trade, military mobility, and the capacity to respond to emergency situations. Virkkunen added that the cross-border nature of these threats requires a capacity for rapid joint action with international partners, especially in a context where hybrid strategies blur the lines between civilian and military infrastructures.
For his part, the Executive Director of ENISA, Juhan Lepassaar, stated that digital dependencies in European critical infrastructures represent a shared operational reality, where interconnected systems expose economies to common risks that require joint responsibility for security.
The transport sector occupies a significant socioeconomic position in the current geopolitical context. ENISA reports on the threat landscape place this segment among the five most affected by cyber incidents over the past two years. Both the railway and maritime sectors present complex environments with multiple actors, similar levels of digitalization, and the common challenge of integrating legacy operational technologies with modern systems without altering safety and reliability standards. The dependence on supply chains and external providers increases exposure to these risks, while its role in military logistics elevates its strategic value. ENISA's NIS360 report indicated that both subsectors show a cybersecurity maturity index below the average in relation to their level of criticality.
During the development of Cyber Europe, critical maritime and railway infrastructures suffered a simulated coordinated attack that caused operational disruptions. Navigation systems and port logistics were compromised, halting the movement of goods and generating collision risks. Concurrently, railway networks experienced disruptions that halted cross-border trains, affecting the transport of passengers and supplies. Transport authorities and ticket sales services were also subject to a data ransom attack that affected administrative management, causing data leaks and disinformation campaigns on social media by hacking activist groups.
This edition has served to test the EU Cybersecurity Crisis Response Plan (Cyber Blueprint), updated in June 2025 to coordinate technical, operational, and political actions in the face of large-scale incidents. Additionally, for the first time, the EU Cybersecurity Reserve, provided for in the EU Cyber Solidarity Regulation and operated by ENISA, was tested, which provides response services through managed and trusted security providers.
After the conclusion of the exercise, ENISA will proceed to conduct a detailed assessment and analysis to identify the weaknesses of the system, the results of which will be compiled in conclusion reports aimed at introducing improvements in the community's preparedness and response processes.